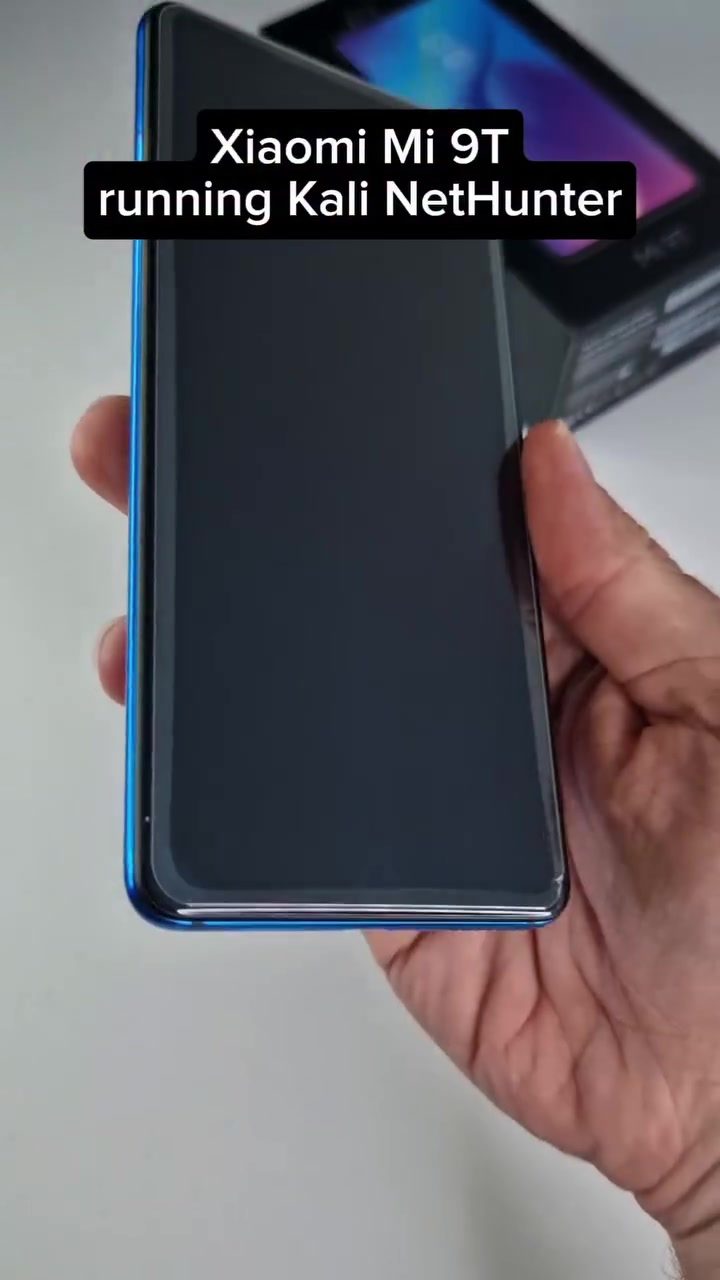
Pocket-Sized Pentesting with a Xiaomi Smartphone
Transform your Xiaomi Mi 9T into a powerful mobile hacking tool with Kali NetHunter. This versatile toolkit is designed for ethical hackers and security professionals, turning a smartphone into a mobile pentesting powerhouse.
Why This Matters
In the ever-evolving landscape of cybersecurity, the ability to test and secure networks on the go is invaluable. Kali NetHunter equips you with a comprehensive suite of tools, making it an essential asset for anyone involved in wireless penetration testing and ethical hacking.
Exploring Kali NetHunter
Turn Your Smartphone into a Pentesting Lab
Portability and Mobility
A key advantage of Kali NetHunter is its portability. The lightweight Xiaomi Mi 9T smartphone can easily fit in your pocket, making it ideal for field operations where mobility is crucial. This enables security professionals to conduct on-site assessments and troubleshoot network vulnerabilities in real-time.
Wireless Attack Testing
Kali NetHunter is specifically designed for wireless attack testing. It allows you to evaluate the security of Wi-Fi networks, Bluetooth, and NFC (Near Field Communication) devices. This capability is particularly useful for pentesters who need to identify and address potential weaknesses in wireless infrastructure.
Full Kali Linux Tools
Popular Hacking Tools
The suite includes a range of powerful tools that are essential for wireless penetration testing:
- Metasploit: A framework for developing and executing exploit code.
- Nmap: A network scanner used to discover hosts and services on a computer network.
- Aircrack-ng: A suite of tools to assess Wi-Fi network security.
- SSH: Secure Shell for remote command-line access.
- Rubber Ducky: A keystroke injection attack tool.
Hosting Server Capabilities
Beyond these tools, Kali NetHunter can also run a hosting server, allowing you to host and manage your own web applications directly from your smartphone. This feature is particularly useful for simulating attacks and testing server security in various scenarios.
Red Team Operations
Real-World Attack Simulation
For red teams, Kali NetHunter provides the capability to simulate real-world attacks. This allows you to test and strengthen defenses against potential cyber threats, ensuring that your systems are resilient against various attack vectors.
Network Auditing
With Kali NetHunter, you can audit networks from anywhere, making it an invaluable tool for security researchers and ethical hackers who need to conduct thorough assessments in the field.
Tools in Action
The demo showcases some of the key tools integrated into Kali NetHunter, particularly focusing on the Bluetooth Arsenal. This suite of tools allows for deep exploration and interaction with Bluetooth devices.
Bluetooth Arsenal
Internal Bluetooth Monitoring
One of the standout features is the ability to put the internal Bluetooth in monitor mode. This allows for detailed analysis and interaction with Bluetooth devices, enabling you to test for vulnerabilities and assess the security of Bluetooth connections.
Bluebinder and Wifipumpkin3
The demo highlights tools like Bluebinder and Wifipumpkin3. Bluebinder is a Bluetooth manipulation toolkit that helps in exploiting vulnerabilities in Bluetooth devices. WiFiPumpkin3, on the other hand, is a rogue access point framework for security testing, allowing you to simulate a fake Wi-Fi network to capture traffic and assess security.
Practical Tips
Setting Up Kali NetHunter
-
Choose the Right Hardware: The Xiaomi Mi 9T, with its powerful Snapdragon processor and large battery, is an excellent choice for running Kali NetHunter. Its efficiency ensures that your toolkit runs smoothly, even during extended field operations.
-
Install Kali NetHunter: Follow the official instructions to install Kali NetHunter on your Xiaomi Mi 9T. Ensure that you have the necessary drivers and firmware updates for optimal performance.
-
Explore the Tools: Familiarize yourself with the various tools available in Kali NetHunter. Metasploit, Nmap, Aircrack-ng, and SSH are just a few of the many tools you can use for different types of penetration testing.
Using Bluetooth Arsenal
-
Enable Bluetooth Monitoring: Use the Bluetooth Arsenal to enable monitor mode. This allows you to capture and analyze Bluetooth traffic, helping you identify potential vulnerabilities.
-
Test with Bluebinder and Wifipumpkin3: Utilize tools like Bluebinder for Bluetooth manipulation and WiFiPumpkin3 for simulating rogue access points. These tools can help you test the security of both Bluetooth and Wi-Fi networks.
-
Automate Scans and Log Data: Customize your workflows to automate scans and log GPS data. This feature is particularly useful for comprehensive network audits, allowing you to export results for desktop visualization and analysis.
Important Takeaways
- Mobility: Kali NetHunter turns your smartphone into a powerful, portable cybersecurity tool, ideal for field operations.
- Wireless Testing: It is a comprehensive toolkit for testing the security of wireless networks, including Wi-Fi, Bluetooth, and NFC.
- Full Kali Linux Tools: It includes a suite of popular hacking tools like Metasploit, Nmap, Aircrack-ng, and SSH, along with hosting server capabilities.
- Red Team Operations: Simulate real-world attacks and strengthen defenses with Kali NetHunter's advanced capabilities.
- Bluetooth Arsenal: Tools like Bluebinder and Wifipumpkin3 provide deep insights into Bluetooth and Wi-Fi security.
Conclusion
The Xiaomi Mi 9T running Kali NetHunter is more than just a smartphone; it's a portable cybersecurity arsenal. By leveraging its mobility, comprehensive toolkit, and advanced features, you can conduct thorough network assessments and simulations, ensuring robust security measures in various environments. Whether you're a pentester, security researcher, or ethical hacker, Kali NetHunter offers the tools and flexibility needed to stay ahead in the ever-changing world of cybersecurity.
Watch the Reel
Questions readers ask
What is Kali NetHunter and how does it work with the Xiaomi Mi 9T?
Kali NetHunter is a suite of tools that transforms the Xiaomi Mi 9T into a portable hacking device. It offers a comprehensive range of wireless penetration testing tools, allowing ethical hackers and security professionals to assess Wi-Fi, Bluetooth, and NFC security on the move.
What are the benefits of using Kali NetHunter with a Xiaomi Mi 9T for security assessments?
Using Kali NetHunter with a Xiaomi Mi 9T provides portability and mobility, making it easy to conduct on-site network vulnerability assessments. The smartphone's compact size allows for discreet and efficient wireless penetration testing, ensuring that security professionals can address issues promptly.
Can Kali NetHunter be used for Bluetooth security testing?
Yes, Kali NetHunter includes tools specifically designed for Bluetooth security testing. This makes the Xiaomi Mi 9T an effective tool for assessing and securing Bluetooth-connected devices, adding another layer to your mobile hacking arsenal.
What kind of wireless penetration testing can be done with Kali NetHunter on a Xiaomi Mi 9T?
With Kali NetHunter, you can perform a wide range of wireless penetration testing tasks, including Wi-Fi security assessments, Bluetooth audits, and NFC vulnerability testing. This toolkit is designed to cover various aspects of wireless security, making it a versatile choice for security professionals.
Is Kali NetHunter suitable for both beginners and experienced security professionals?
Kali NetHunter is particularly well-suited for experienced security professionals due to its advanced features and comprehensive toolkit. However, with the right guidance, beginners can also benefit from the suite by learning and practicing ethical hacking techniques in a controlled environment.
How does Kali NetHunter help in on-site network vulnerability assessments?
Kali NetHunter enables on-site network vulnerability assessments by providing a mobile, discrete platform for testing wireless security. Security professionals can use the Xiaomi Mi 9T to quickly identify and address vulnerabilities in Wi-Fi, Bluetooth, and NFC networks, ensuring that issues are resolved efficiently.
What is the role of Kali NetHunter in mobile Wi-Fi security assessment?
Kali NetHunter plays a crucial role in mobile Wi-Fi security assessment by offering a range of tools specifically designed for testing and securing wireless networks. The suite allows security professionals to identify weak points in Wi-Fi security and implement necessary measures to enhance protection, making it an essential tool for mobile pentesting.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.