Software Security
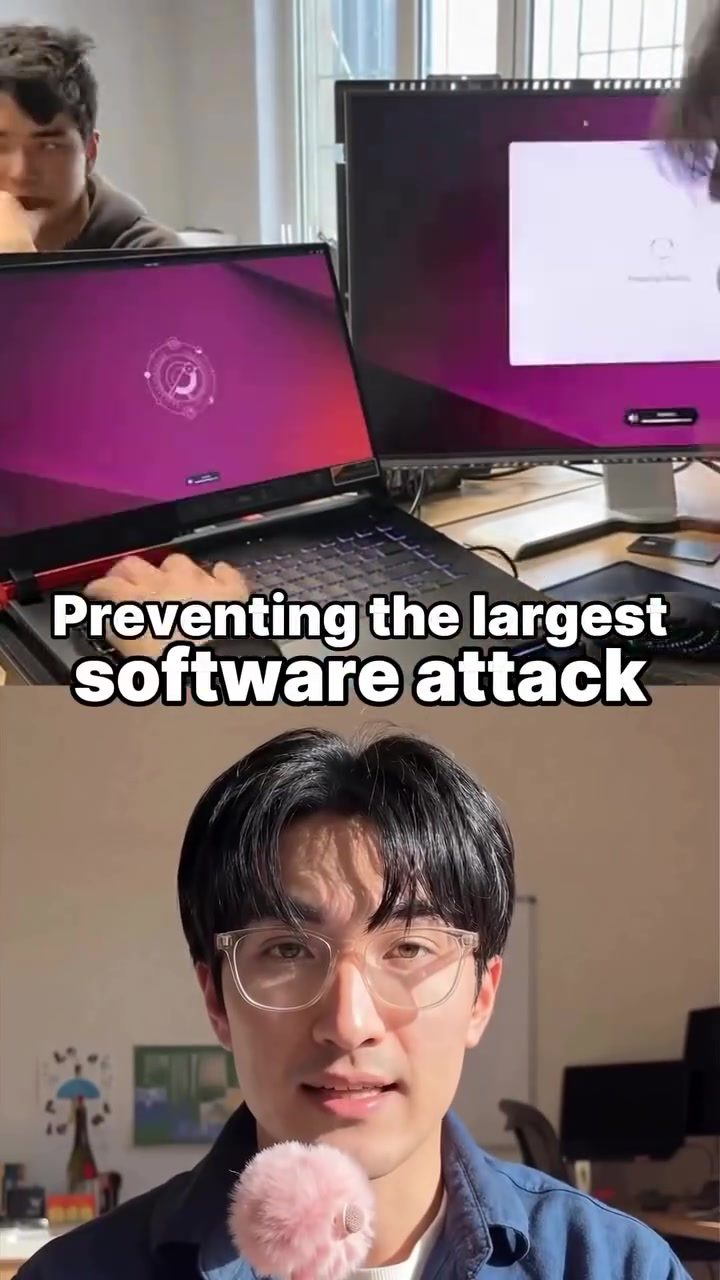
Software supply chain attacks pose a significant threat to critical infrastructure. Microsoft engineer Andres Freund's detection of a half-second delay in SSH logins prevented a major software supply chain attack, highlighting the importance of vigilance in software security.
Why This Matters
Critical infrastructure—such as banking systems, government operations, and corporate networks—relies heavily on software. When these systems are compromised, the consequences can be catastrophic. The incident involving XZ Utils, a small but widely used open-source package, underscores how even minor components can become critical vulnerabilities.
Main Discussion
The XZ Utils Incident
Detection and Response
Andres Freund, a Microsoft engineer, detected an unusual half-second delay in SSH logins on a Linux test server. This subtle anomaly prompted an investigation that revealed extra CPU usage linked to XZ Utils, a tiny open-source package. Freund's keen observation prevented a potential disaster by identifying the issue before it could spread.
The Scope of the Threat
XZ Utils is used across various sectors, including banking, corporate networks, and government systems. An attacker had spent years earning trust within the community, inserting a backdoor that could unlock affected machines with a private key. The implications of such a breach are vast, as it could compromise sensitive data and critical operations.
The Importance of Trust Verification
The incident highlights the necessity of continuous trust verification in open-source systems. Open systems create immense value by fostering collaboration and innovation, but they also require rigorous security measures. Trust must be continuously verified to ensure that dependencies do not become vulnerabilities.
The Role of Open-Source Software
Benefits and Risks
Open-source software is a cornerstone of modern technology. It allows for rapid development, community collaboration, and cost-effectiveness. However, it also introduces risks, especially when critical infrastructure relies on these systems. The XZ Utils incident serves as a reminder that even the smallest components can pose significant threats.
Community Trust and Security
The open-source community thrives on trust. Developers and users rely on the integrity of the software they use. However, this trust can be exploited by malicious actors. Ongoing verification and monitoring are essential to ensure that the software remains secure and reliable.
Market Risk Beyond Price Risk
Understanding Market Risk
Market risk is often associated with price fluctuations, but it encompasses much more. Critical infrastructure failures can have far-reaching consequences, affecting not just financial markets but also national security and public safety. Understanding and mitigating these risks is crucial for maintaining stability and resilience.
Dependency Management
Many critical systems rely on dependencies that are often overlooked. These dependencies can become points of failure if not properly managed. The XZ Utils incident underscores the importance of monitoring and verifying these dependencies to ensure they do not introduce vulnerabilities.
Practical Tips
Monitoring and Alerts
Implement Robust Monitoring
Deploying robust monitoring systems can help detect anomalies early. Tools that track CPU usage, login times, and other metrics can alert teams to potential issues before they escalate. This proactive approach can prevent major incidents and mitigate risks.
Set Up Alerts for Unusual Activity
Alerts for unusual activity, such as sudden spikes in CPU usage or login delays, can help identify problems quickly. Automated alerts can notify security teams in real-time, allowing for prompt investigation and resolution.
Regular Audits and Verification
Conduct regular audits of dependencies and their sources. Ensure that all components are verified and trusted. This includes checking for updates, patches, and security advisories.
Community Engagement
Engage with the open-source community to stay informed about potential vulnerabilities and security updates. Participating in forums, mailing lists, and conferences can provide valuable insights and early warnings about potential threats.
Important Takeaways
- Vigilance is Key: Even small anomalies can indicate significant security issues. Continuous monitoring and prompt investigation are crucial.
- Trust Must Be Verified: Open-source systems create immense value, but trust must be continuously verified to prevent exploitation.
- Dependency Management: Overlooked dependencies can become critical vulnerabilities. Regular audits and verification are essential.
- Community Engagement: Engaging with the open-source community can provide early warnings and valuable insights.
Conclusion
The incident involving XZ Utils serves as a stark reminder of the importance of software security. Critical infrastructure is at risk from overlooked dependencies, making continuous trust verification and robust monitoring essential. By staying vigilant and proactive, organizations can protect themselves from potential threats and ensure the reliability of their systems.
Watch the Reel
Questions readers ask
What is a software supply chain attack and why is it a significant threat?
A software supply chain attack involves compromising an organization's software or hardware supply chain, which can introduce vulnerabilities into critical infrastructure. These attacks are significant threats because they can disrupt vital systems, such as banking or government operations, by infiltrating widely-used software components.
What role did the half-second delay in SSH logins play in preventing a major attack?
The half-second delay in SSH logins was a crucial indicator that alerted Microsoft engineer Andres Freund to unusual activity. This small but noticeable delay helped Freund identify a potential software supply chain attack, allowing for timely intervention and prevention of a major security breach.
How did the XZ Utils incident highlight the risks of open-source software?
The XZ Utils incident involved a widely-used, open-source package that was exploited to introduce vulnerabilities. This incident underscored how even small, seemingly innocuous open-source components can become major entry points for attackers, affecting critical infrastructure and corporate networks.
What measures can be taken to enhance the security of critical infrastructure?
Enhancing the security of critical infrastructure involves implementing robust monitoring systems, such as those that detect unusual delays or anomalies. Regular audits of software components, including open-source packages, and maintaining vigilance through continuous monitoring can help identify and mitigate potential threats.
Why is vigilance crucial in securing critical infrastructure?
Vigilance is crucial because it allows for the early detection of anomalies and potential threats. By staying alert and implementing proactive security measures, organizations can respond swiftly to incidents like the XZ Utils case, thereby protecting vital systems from catastrophic attacks.
How can organizations protect themselves from software supply chain attacks?
Organizations can protect themselves by ensuring that all software components, especially open-source packages, are thoroughly vetted and regularly updated. Implementing strict security protocols, conducting regular security audits, and fostering a culture of vigilance can significantly reduce the risk of supply chain attacks.
What was the significance of Andres Freund's detection in the context of supply chain security?
Andres Freund's detection of the half-second delay in SSH logins was significant because it demonstrated the importance of proactive monitoring in identifying potential supply chain attacks. His vigilance played a key role in preventing a major attack, highlighting the need for continuous monitoring and prompt response to anomalies.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.