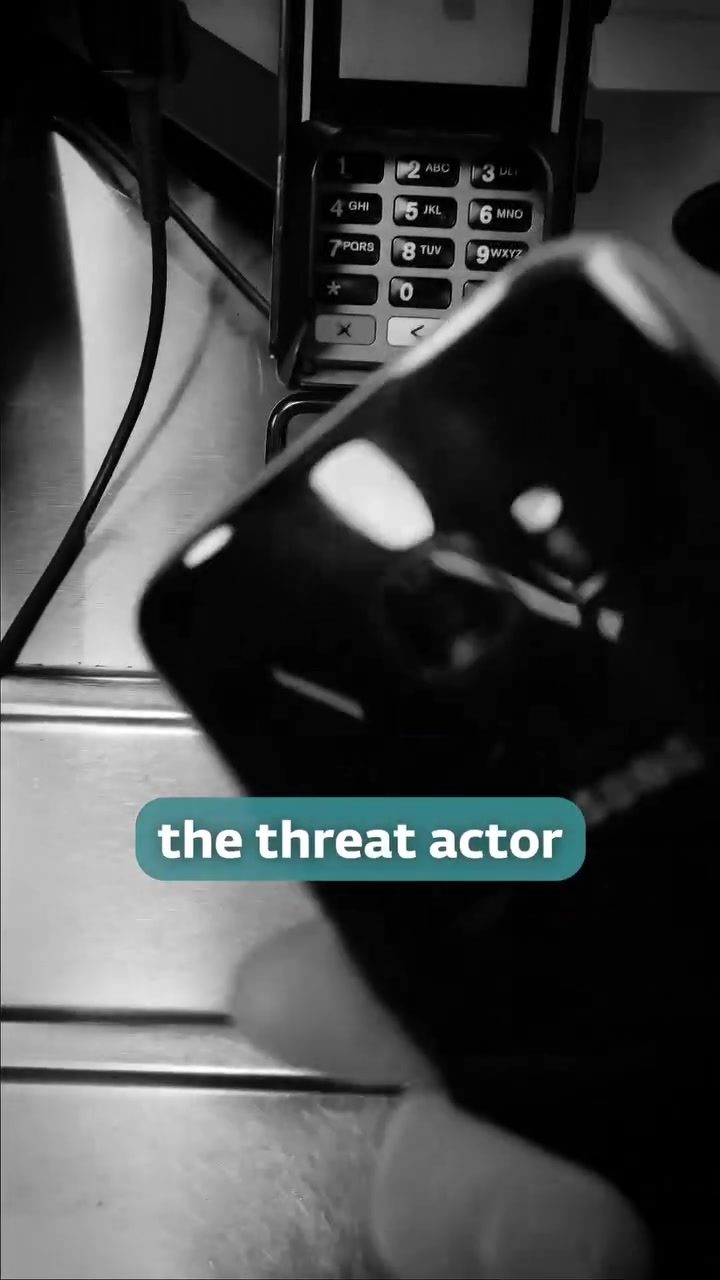
ATM Skimming and the Threat of NFC Malware
New Android malware, NGate, allows criminals to exploit NFC technology to steal from ATMs and retail terminals. Here's how it works and what you need to know to protect yourself.
Context / Why This Matters
In today's increasingly digital world, the convenience of contactless payments has become the norm. However, this convenience comes with risks, particularly when it comes to the security of our payment cards. A newly identified Android malware, dubbed "NGate," is exploiting NFC (Near Field Communication) technology to steal payment data and facilitate unauthorized withdrawals and transactions. Understanding the mechanics of this threat is crucial for safeguarding personal finances in an age where technology is both our greatest ally and our most significant vulnerability.
Main Discussion
The Mechanics of NGate Malware
NGate malware operates by relaying NFC data from a victim's payment card to an attacker's smartphone. This process involves several key steps:
- Initial Infestation: The malware gains access to a victim's mobile phone, often through phishing or other social engineering tactics.
- Data Relay: Once installed, the malware can scan and relay NFC data from the victim's payment card to the attacker's device.
- Transaction Emulation: The attacker's smartphone can then emulate the victim's card, allowing them to perform unauthorized transactions at ATMs or retail terminals. This includes making purchases or withdrawing cash.
The use of two Android smartphones can extend the range between the card and the terminal, making the process more covert and difficult to detect.
Common Scenarios
ATM Withdrawals
For an attacker to withdraw money from an ATM, they typically need to:
- Have physical access to the victim's payment card.
- Have a compromised mobile device with NGate malware installed.
- Use a second smartphone to emulate the victim's card.
If the attacker has already obtained the necessary bin (the first six digits of a card number), they can clone the contactless transaction and complete the withdrawal. If not, they may attempt to loot the victim's account through phishing or engineering methods.
Retail Transactions
In retail environments, attackers can use the same technique to make purchases. By relaying the victim's card data to their own device, they can complete transactions at terminals.
Crowded Area Attacks
Another disturbing tactic involves scanning wallets and cards in crowded areas, such as public transportation or busy shopping districts. Attackers can use the same relay method to capture card data through bags and backpacks.
Practical Tips
While the threat of NGate malware is alarming, there are steps you can take to mitigate the risk:
- Use Protection: Ensure your mobile device is equipped with reliable antivirus software.
- Monitor Activity: Regularly check your bank statements and transaction history for any unauthorized activity. Set up alerts for unusual transactions.
- Secure Your Card: Keep your payment cards in a shielded wallet or protective sleeve that blocks NFC signals, making it harder for attackers to scan your card data.
- Update Your Device: Keep your Android device and all apps up to date with the latest security patches.
- Avoid Suspicious Links and Downloads: Be cautious of phishing attempts and avoid downloading apps from unverified sources.
Important Takeaways
The emergence of NGate malware highlights a new and concerning threat to contactless payment technologies. While the convenience of NFC payments is undeniable, it is essential to recognize the risks and take proactive measures to safeguard personal information. By staying informed and vigilant, consumers can better protect themselves from this and similar threats.
Conclusion
The rise of NGate malware underscores the evolving landscape of cybercrime, where traditional security measures may no longer be sufficient. As technology advances, so do the tactics of cybercriminals. However, by understanding the mechanics of these threats and taking proactive steps to secure personal information, individuals can significantly reduce their risk of falling victim to such attacks. Whether at an ATM or a retail terminal, vigilance and protective measures are key to maintaining financial security in an increasingly digital world.
Watch the Reel
Questions readers ask
What is NGate malware and how does it work?
NGate is a type of Android malware designed to exploit Near Field Communication (NFC) technology. It allows criminals to use smartphones to read and steal payment card data from NFC-capable cards. Once the data is stolen, it can be used to make unauthorized transactions at ATMs and retail terminals.
How can NGate malware be used for ATM skimming?
NGate malware enables criminals to perform ATM skimming by using an infected smartphone to capture payment card data when it is tapped against a contactless payment terminal. This data is then used to create cloned cards, which criminals can use to withdraw cash from ATMs.
What are the risks of using contactless payment methods?
While convenient, contactless payment methods can expose users to risks, such as data theft. NGate malware is a prime example, as it can steal payment card data through NFC technology. Users should be aware of these risks and take appropriate measures to protect their financial information.
Can NGate malware infect any Android device?
NGate malware specifically targets Android devices. While all Android devices with NFC capabilities are potentially at risk, not all devices may be equally vulnerable, depending on the version of Android and any installed security software.
How can I protect my payment card data from NFC malware?
To protect your payment card data from NFC malware, it's important to keep your smartphone and apps up-to-date, use a reliable security app, and be cautious of unfamiliar apps or downloads. Additionally, consider using a protective cover or sleeve for your NFC-capable cards to block NFC signals when not in use.
What should I do if I suspect my payment card data has been compromised?
If you suspect your payment card data has been compromised, notify your bank immediately to report the potential fraud. Request a new card and monitor your account for any unauthorized transactions. Changing your PIN and account passwords can also help secure your finances.
How do uninfected smart phones and money machines work together to protect against NGate malware?
Uninfected smartphones and ATMs can help prevent NGate malware attacks by ensuring that both the device and the ATM are running up-to-date software. This includes the latest security patches and anti-virus software on the smartphone and regular updates and security checks on the ATM. It's important to verify that your smartphone and the ATM are genuine.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.