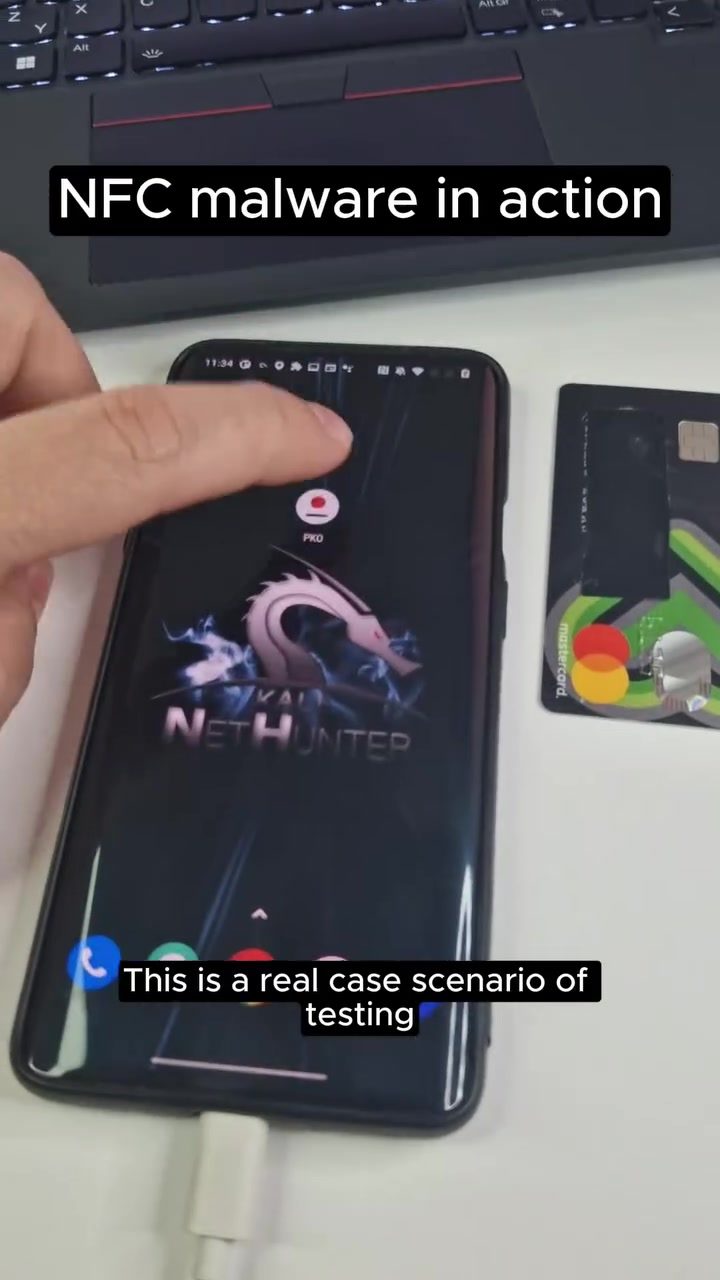
NFC Malware: The Threat to Mobile Payment Security
Near-field communication (NFC) technology has revolutionized the way we make payments, offering convenience and speed. However, this convenience comes with a hidden danger: NFC malware. This type of malware can steal sensitive data from contactless payment cards, putting users at significant risk. Understanding how NFC malware operates and how to protect against it is crucial for anyone who uses mobile payment systems.
Why This Matters
Mobile payment systems have become ubiquitous, thanks to the convenience and speed of NFC technology. However, the rise of NFC malware poses a serious threat to this convenience. Malware can exploit NFC to steal sensitive data from contactless payment cards, leading to financial loss and identity theft. Being aware of the risks and taking preventive measures is essential for safeguarding personal and financial information.
Understanding NFC Malware
How NFC Malware Works
NFC malware operates by exploiting the way NFC technology works. When a smartphone is used to make a payment, it communicates with the payment terminal using NFC. Malware can intercept this communication, stealing sensitive data such as card numbers, expiry dates, and PINs. This data can then be relayed to the attacker's server, allowing them to make unauthorized transactions.
In a real-world scenario, NFC malware can impersonate a legitimate banking app. It may prompt the user to place their payment card on the back of their smartphone for verification. During this process, the malware transmits the card data to the attacker's server, along with the PIN. The attacker can then use this information to withdraw money from an ATM, as the transaction appears legitimate due to the session and PIN data.
The NFC Attack Process
- Initial Contact: The malware impersonates a legitimate banking app, asking the user to place their payment card on the back of their smartphone.
- Data Transmission: The malware reads the data from the contactless card and sends it to the attacker's server, along with the PIN.
- Data Relay: The attacker uses the stolen data to make unauthorized transactions, such as withdrawing money from an ATM.
- Verification: The attacker can verify the traffic using tools like Wireshark to ensure the data is being transmitted correctly.
Practical Tips for Protection
Preventing NFC malware attacks involves a combination of awareness and best practices. Here are some steps to safeguard your mobile payments:
Download from Trustworthy Sources
Always download apps from official app stores or trusted sources. Avoid downloading apps from third-party websites or unknown sources, as they may contain malware.
Avoid Unusual Verification Methods
Be cautious of any app that asks you to place your payment card on the back of your smartphone for verification. Legitimate banking apps and payment systems do not require such actions.
Protect Your PIN
Never share your PIN with anyone, and avoid entering your PIN on unauthorized devices. Additionally, cover the keypad when entering your PIN to prevent shoulder surfing.
Stay Informed
Regularly update your knowledge about the latest threats and security practices. Websites like velosecurity.com and welivesecurity.com offer valuable information and resources on how to protect against NFC malware and other cyber threats.
Important Takeaways
NFC malware represents a significant threat to the security of mobile payments. By understanding how it operates and taking preventive measures, users can protect their sensitive data and avoid financial loss. Key points to remember include:
- Avoid Unauthorized Apps: Only download apps from trusted sources.
- Be Cautious of Unusual Requests: Do not place your card on the back of your smartphone for verification.
- Protect Your PIN: Keep your PIN confidential and avoid sharing it.
- Stay Informed: Regularly update your knowledge on cybersecurity threats and best practices.
Conclusion
NFC malware is a real and growing threat to mobile payment security. By being aware of how it operates and taking proactive steps to protect yourself, you can safeguard your financial information and prevent unauthorized transactions. Stay vigilant, follow best practices, and stay informed to ensure the security of your mobile payments.
Watch the Reel
Questions readers ask
What exactly is NFC malware and how does it target contactless payment systems?
NFC malware is a type of malicious software designed to exploit the near-field communication technology used in contactless payment systems. It targets the wireless data exchange between mobile devices and payment terminals, intercepting and stealing sensitive information such as card numbers and PINs. This makes it a direct threat to the security of mobile payment data.
How does NFC malware lead to unauthorized transactions?
NFC malware intercepts the communication between a user's mobile payment system and the payment terminal. By capturing the necessary data, the malware allows unauthorized individuals to mimic the user's payment information, leading to fraudulent transactions and financial loss. This makes understanding and preventing NFC malware crucial for mobile payment security.
Can NFC malware affect both Android and iOS devices?
Yes, NFC malware can potentially affect both Android and iOS devices that support NFC technology. However, Android devices are generally considered more vulnerable due to the broader range of app sources and permissions. iOS devices, with their more controlled app ecosystem, have a lower risk, but are not entirely immune.
What are NFC relay attacks and how do they relate to NFC malware?
NFC relay attacks occur when malware intercepts and relays communication between a legitimate payment card and a payment terminal. This allows a fraudster to make a payment using a stolen card without needing the physical card. This method can be used in conjunction with NFC malware to steal and use payment data, making it a significant threat to secure contactless payments.
What are some effective methods to prevent NFC malware?
To prevent NFC malware, users should keep their mobile operating systems and apps up to date, use reputable app stores, and be cautious of apps requesting excessive permissions. Additionally, enabling device encryption and using secure mobile payment apps can help protect mobile payment data from potential NFC malware threats.
How can users detect if their device has been compromised by NFC malware?
Detecting NFC malware can be challenging, but users should be vigilant for unusual activity, such as unexpected financial transactions or apps behaving strangely. Regularly monitoring financial statements, installing reliable security software, and performing routine security checks can help in identifying and mitigating the risks associated with NFC malware.
What steps can be taken to ensure NFC payment security?
To ensure NFC payment security, users should enable NFC only when necessary and use trusted payment applications. It's also important to keep the device's software up to date, and avoid using public or unsecured wireless networks for mobile payments. Regularly reviewing bank statements and setting up alerts for unusual activity can provide an additional layer of protection against NFC malware.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.