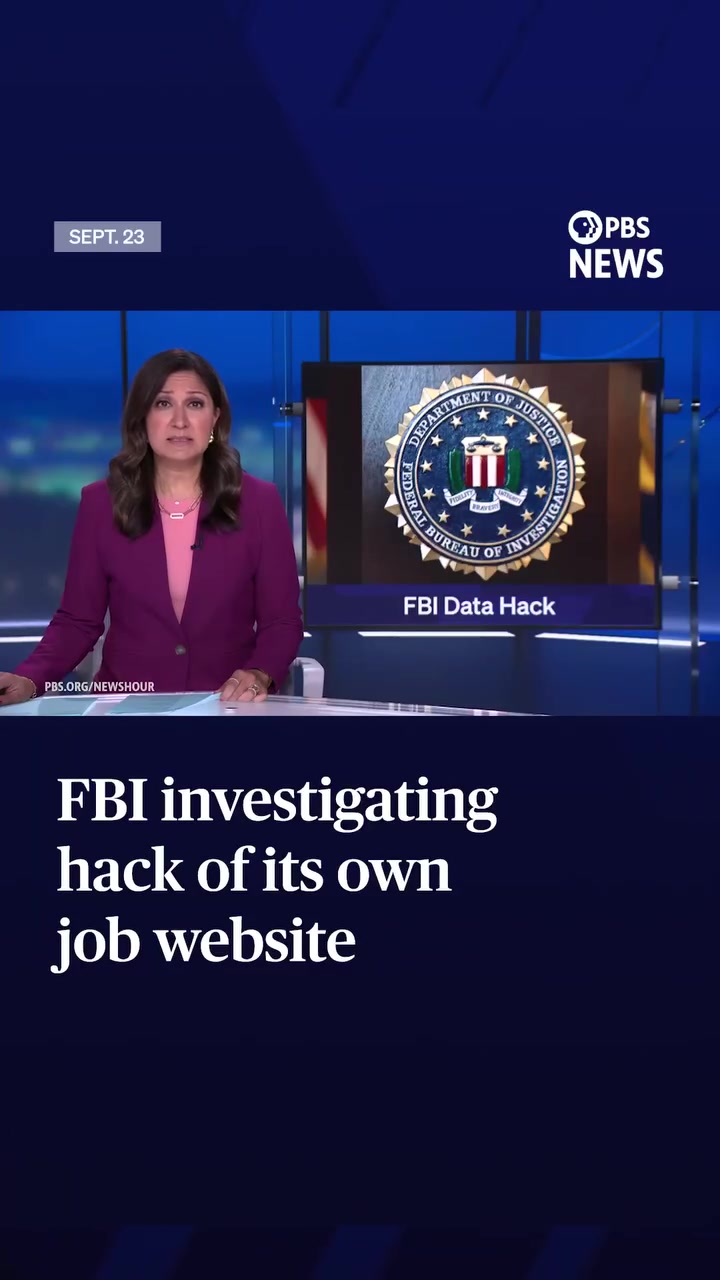
The Federal Bureau of Investigation (FBI) is actively investigating Shiny Hunters, a criminal hacking group claiming to have stolen sensitive data from the bureau’s job website. The group allegedly obtained personnel information for thousands of FBI officials., The FBI has been made aware of the situation by the group, which it described as a criminal enterprise, and issued a strongly worded statement committing to an active and aggressive investigation.
The data heist
The FBI has confirmed that it is investigating a cybercriminal enterprise group’s claim of compromising and promptly removing sensitive data from the department's job website. The FBI describes it as a hack involving a group called Shiny Hunters. The FBI disclosed that it was “aware of a cybercriminal enterprise group claiming a compromise and that we are actively and aggressively investigating this matter”. The FBI did not explicitly confirm whether the breach indeed occurred, as it did not specify the precise nature of the compromised data. However, Shiny Hunters asserted that it obtained personnel information for thousands of FBI officials. Despite their cyber offensives, Shiny Hunters has not yet posted any sample data on the dark web; however, the group is well known for previously hacking high-profile targets, including such incidents as the theft of 788 million records of 10.8 million users of car sharing company Turo. On September 23 — when the information was still being processed — the FBI had not altered or removed an advisory concerning the group, and the organization’s job portal remained offline.
Cybercriminals shift targets
In recent years, cybercriminals have shifted their focus from traditional targets like financial institutions and large corporations to government and law enforcement agencies. In some cases, hackers target government websites and databases looking for sensitive data that can be sold on the dark web. In the FBI’s recent incident, a hacking group called Shiny Hunters allegedly obtained personnel information for thousands of FBI officials from the bureau’s job website, highlighted the evolving nature that cybercriminals are undertaking to breach government entities. Although the FBI has not specified the precise nature of the compromised data, reporting noted that the data breach seemed to involve the FBI's job website. FBI’s official statement said the bureau was "aware of a cybercriminal enterprise group claiming a compromise and that we are actively and aggressively investigating this matter".
Uncertain longevity for online job portals
Many cybercriminal groups like Shiny Hunters are motivated by financial gain and will sell the stolen data on the dark web. When this occurs, the sale of sensitive data can result in identity theft, blackmail, and other forms of cybercrime. They may also use the stolen information to launch further attacks on the targeted organization. The FBI hack shows that job websites and portals are vulnerable to data breaches. This is a wake-up call to organizations and individuals who post personal data on job websites. Data breaches can cause significant reputational damage to an organization, which erodes the trust of its customers and partners. Regulatory bodies, such as the Federal Trade Commission, may also levy fines and penalties for data breaches, which could cost millions of dollars. These financial losses can affect the long-term viability of the organization.
Government websites remain high-risk targets
Government entities continue to be prime targets for hackers. The FBI has been the subject of numerous cyberattacks in recent years, including the breach of its Law Enforcement Enterprise Portal (LEEP). This attack occurred in 2018 and resulted in the theft of sensitive data, including personal information belonging to law enforcement officers and agents. The breaches have resulted in the theft of sensitive information, including personal and financial data. Cybercriminals use the stolen information for various purposes, such as identity theft, blackmail, and other forms of cybercrime. The recent hack at the FBI shows that it is essential to prioritize cybersecurity and protect sensitive data.
The rise of cybercrime groups
According to a report by the FBI’s Internet Crime Complaint Center (IC3), the number of cybercrime complaints received by the FBI in 2022 was up 6.9% from the previous year, and the total losses reported by victims were up 36%. As cybercriminals continue to refine their tactics, it is essential for government and law enforcement agencies to stay vigilant in protecting sensitive data. The rise of cybercrime groups like Shiny Hunters has led to an increase in the number of cyberattacks targeting government entities. Cybercriminals employ sophisticated tactics to breach the defenses of government agencies, often using malware, phishing, and social engineering to gain access to sensitive data and systems. Government agencies have become prime targets for cybercriminals because they hold vast amounts of sensitive information, including personal and financial data, national security secrets, and other confidential information. Additionally, government cybersecurity spending has lagged behind the private sector, leaving government agencies vulnerable to cyberattacks.
Tips for safe job hunting online
Applying for a position online is a common practice in the contemporary job market. However, the recent FBI incident should serve as a cautionary tale for job seekers. Here are some safety tips for online job portals:
- Secure your data: Keep your sensitive information, such as personal identification and financial details, to a minimum. Avoid using personal email addresses, unless the employment opportunity can be independently verified, and refrain from sharing personal photos or anything that can be used to compromise personal identity.
- Vetting the cybersecurity protocols: Look for job portals that prioritize user safety. Typically, they should use the latest in encryption and multi-factor authentication. Verify their cybersecurity protocols and protections against hacking and data breaches.
The FBI's response and a call for vigilance
The FBI should be commended for acknowledging the breach and promptly addressing the claim. However, the incident underscores the responsibility of the government to take precautionary measures in protecting sensitive data. The FBI should consider including cybersecurity tips for applicants and employees and improve the cybersecurity strategies of the portal. The bureau should also endeavor to provide job seekers with up-to-date information about the job portal's status and any potential security breaches. By taking these steps, the FBI can rebuild trust with the public and ensure that its job portal remains a safe and secure platform for job seekers.
Watch the Reel
Questions readers ask
What exactly did Shiny Hunters claim to have stolen from the FBI's job portal?
Shiny Hunters claimed to have obtained personnel information for thousands of FBI officials. This includes sensitive data that could potentially be used for identity theft, blackmail, or further cyber attacks. However, the FBI has not confirmed the exact nature of the compromised data.
Why are government agencies like the FBI becoming more frequent targets for cybercriminals?
Government agencies are increasingly attractive targets for cybercriminals because they hold sensitive data that can be sold on the dark web. The FBI job portal hack highlights this shift, as hackers are moving away from traditional targets like financial institutions and large corporations. This trend shows that cybercriminals are evolving their tactics to breach government entities.
What does it mean that Shiny Hunters has not posted any sample data on the dark web yet?
It means that, as of the latest information, Shiny Hunters has not provided any evidence or samples of the data they claim to have stolen. This could indicate that they are still processing the data, negotiating with buyers, or perhaps even bluffing. It's also possible that the FBI's aggressive investigation is deterring them from releasing any information.
How has the FBI responded to the alleged data breach?
The FBI has issued a strongly worded statement confirming that they are actively and aggressively investigating the matter. They have described Shiny Hunters as a criminal enterprise and have committed to a thorough investigation. However, the FBI has not explicitly confirmed whether the breach indeed occurred or specified the precise nature of the compromised data.
What kind of impact could this data breach have on the FBI and its officials?
A data breach of this nature could have significant consequences. If the stolen data includes personal information, it could lead to identity theft, blackmail, or other forms of cybercrime targeting the affected officials. Additionally, the breach could cause reputational damage to the FBI, eroding public trust in the agency's ability to protect sensitive information.
Can other organizations learn from this incident to protect their job portals?
Yes, this incident serves as a wake-up call for organizations and individuals who post personal data on job websites. It underscores the vulnerability of online job portals to data breaches. Organizations should review and strengthen their cybersecurity measures to prevent similar incidents and protect sensitive information.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.